Cloud
Cloud Security Best Practices Every Business Should Follow
Quick Answer
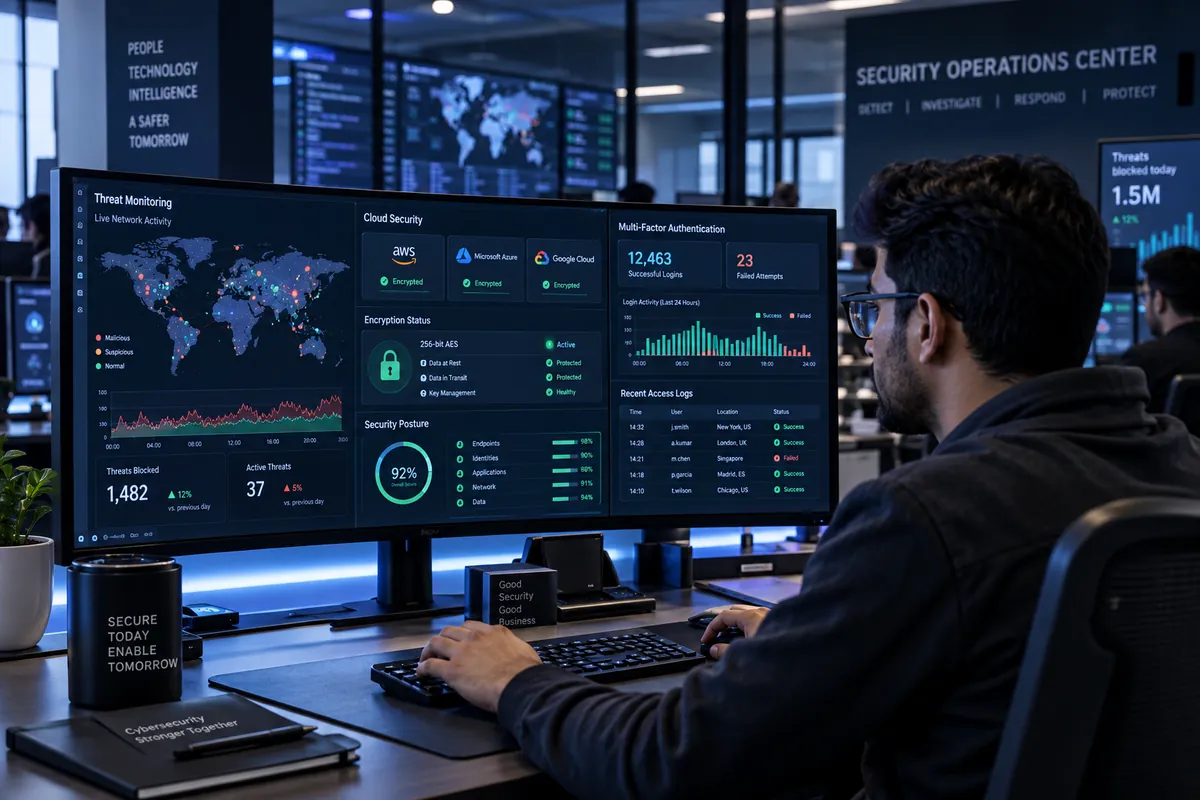
The most important cloud security practices are enforcing multi-factor authentication, granting least-privilege access, encrypting data, keeping storage and databases private, logging and monitoring activity, patching regularly, taking tested backups and having an incident response plan. Most cloud breaches come from misconfiguration, not provider failures.
Introduction
Cloud providers secure their data centres and core infrastructure. Everything you configure on top, including users, permissions, networks, storage and applications, is your responsibility. This shared responsibility model is where most incidents begin.
The practices below cover the controls that prevent the majority of real-world cloud security problems.
Lock down identity first
Compromised credentials are a leading cause of breaches. Protect accounts before anything else.
- Enable multi-factor authentication for every user, especially administrators.
- Do not use the root or owner account for daily work.
- Grant least-privilege roles and review them every quarter.
- Use short-lived credentials and roles for applications instead of long-lived keys.
- Remove access immediately when people leave.
Protect data
Encrypt data at rest and in transit, which major providers make straightforward. Keep storage buckets and databases private by default, and use secrets managers instead of storing passwords and API keys in code or configuration files.
Control the network
Place databases and internal services in private subnets, expose only what must be public, restrict administrative access, and use a web application firewall in front of public applications.
Log, monitor and alert
Enable audit logging for account activity, keep logs in a protected location, and set alerts for unusual events such as new admin users, disabled logging, public storage changes or spending spikes. Logs are what let you understand and contain an incident.
Patch, back up and prepare
Keep operating systems, containers and dependencies updated, scan for vulnerabilities, and take automated backups stored separately from production. Test restores regularly. Write a simple incident response plan: who is contacted, how access is revoked, how systems are restored and how customers or regulators are informed, including obligations under India's data protection rules.
Convert security recommendations into accountable controls
Start with a list of accounts, data stores, applications, external connections and people who can change production. Use that inventory to assign owners and identify the actions that could expose data or interrupt a critical service. The right control depends on the workload and information involved, so treat a checklist as a starting point rather than proof of compliance.
For each important system, test multifactor access, least privilege, encryption configuration, logging, backup restoration and incident contacts. Review changes when staff roles shift and when a new vendor receives access. Pair these steps with the cloud migration checklist, cloud provider comparison and Vaqnova’s cloud service.
Run a tabletop exercise for a lost credential or unavailable database. Confirm who can isolate access, restore data and communicate with affected users. Security depends on people and operating procedures as well as provider features; a managed service does not remove the customer’s responsibility to configure and review it.
Summary
Key Takeaways
- Most cloud incidents are caused by misconfiguration and stolen credentials.
- MFA and least privilege are the highest-value controls.
- Keep data private and encrypted, and store secrets in a secrets manager.
- Logging, alerting and tested backups turn incidents into recoverable events.
Pitfalls
Common Mistakes to Avoid
- Public storage buckets containing customer data.
- API keys committed to source code repositories.
- Shared admin accounts without MFA.
- Backups that have never been restored.
FAQ
Frequently Asked Questions
What is the shared responsibility model?
The provider secures the physical infrastructure and core services; the customer secures identities, configurations, data and applications built on top.
Do small businesses need cloud security tools?
Yes, but the built-in tools from your provider, configured well, cover most needs: MFA, IAM, encryption, logging and alerts.
How often should access be reviewed?
At least quarterly, and immediately when someone changes role or leaves the company.
Should we get a security audit?
A periodic configuration review and penetration test are worthwhile, especially before launching a product that handles sensitive or payment data.
Wrap-up
Final Thoughts
Cloud security is mostly about getting the fundamentals right and keeping them right. Strong identity controls, private and encrypted data, monitoring and tested recovery will prevent or contain the vast majority of incidents.
References
Sources
Let's talk
Build Your Next Digital Product
Vaqnova can review your cloud configuration against these practices and fix the gaps before they become incidents.
Talk to Our Team